PHP releases emergency fixes for two critical vulnerabilities
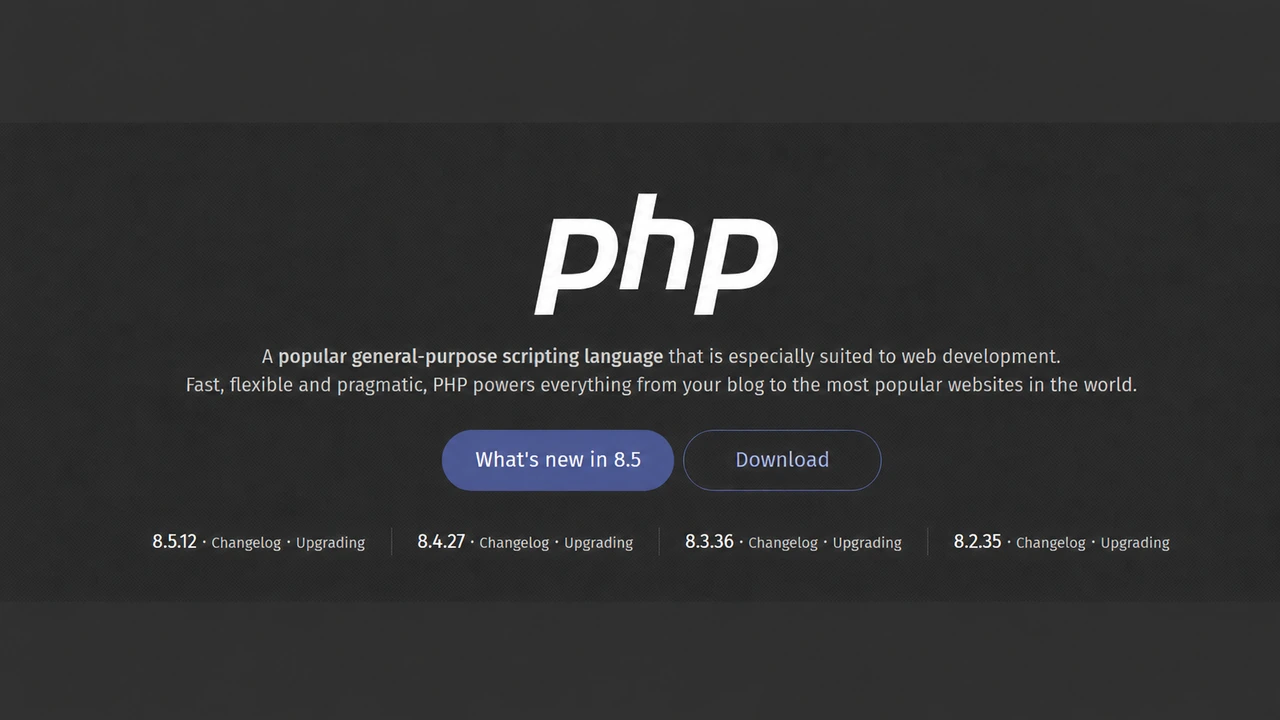
The PHP security team released PHP 8.2.35, 8.3.36, 8.4.27, and 8.5.12 on October 21, 2026, fixing two critical vulnerabilities rated 9.2 on the CVSS v4.0 scale.
The official security advisory confirms that the flaws can enable unauthenticated remote code execution and urges immediate updates. Configuration workarounds do not provide complete protection.
Reuters reported the risk ahead of the release; the fixes and technical details are now public.
More Security and Website News
Get cybersecurity alerts, WordPress updates, and technology coverage from Fix Gaming Channel.
Join Our Newsletter
Stay updated with the latest interviews, previews, security alerts, and gaming news.
Why WordPress sites should pay attention
WordPress runs on PHP, but these are PHP runtime flaws, not WordPress core vulnerabilities. Updating WordPress, themes, or plugins does not update the PHP version supplied by your host. Not every WordPress installation is automatically exploitable: risk depends on its PHP version, configuration, and application behavior. Other PHP-based platforms may also be affected.
Affected versions and released fixes
The official advisories list earlier releases in each of these four supported PHP branches as affected. CVE-2026-109618 involves corrupted request state after memory exhaustion; CVE-2026-109619 involves state that remains accessible after its memory is freed.
What site owners should do now
Check which PHP version your site uses and ask your host to confirm that both fixes are installed, either through the patched release or an equivalent vendor backport. Keep a recent backup. On managed hosting, the provider may handle deployment; self-managed server owners must arrange the update themselves.
For PHP 8.1 and older, check vendor support or move to a supported branch. Temporary mitigations are not a substitute for complete patches.
Related Reading
WordPress 7.0.2 Emergency Update Fixes Critical Security Issue
Apple Patches CoreGraphics Zero-Day Exploited in Targeted Attacks
OpenCode Console Breach May Have Exposed AI API Keys
Written by Robelle Veligano for Fix Gaming Channel.
Send interview pitches, corrections, tips, or developer stories to contact@fixgamingchannel.com.
Support independent games coverage on Ko-fi.